


- Joined
- Jun 13, 2020
- Messages
- 8,119
- Reaction score
- 1,131
- Points
- 212
- Awards
- 2
A likely Russian threat group tracked as GreyVibe has been using AI-generated lures and a rich set of custom malware tools to target entities in the military, government, civilian, and business sectors. The cyberespionage campaign has been active since at least August 2025 and appears to align with Russian state interests, although researchers cannot confidently classify it as a nation-state operation. Cybersecurity company WithSecure discovered the activity in January this year and determined that its focus is on Ukrainian or Ukraine-related organizations. The link to a Russian-speaking threat actor is supported by the language for the malware panels, comments in code artifacts, and command-and-control (C2) server time configured to UTC+3 (Moscow time). According to the researchers, GreyVibe has used several attack chains against its targets, including:
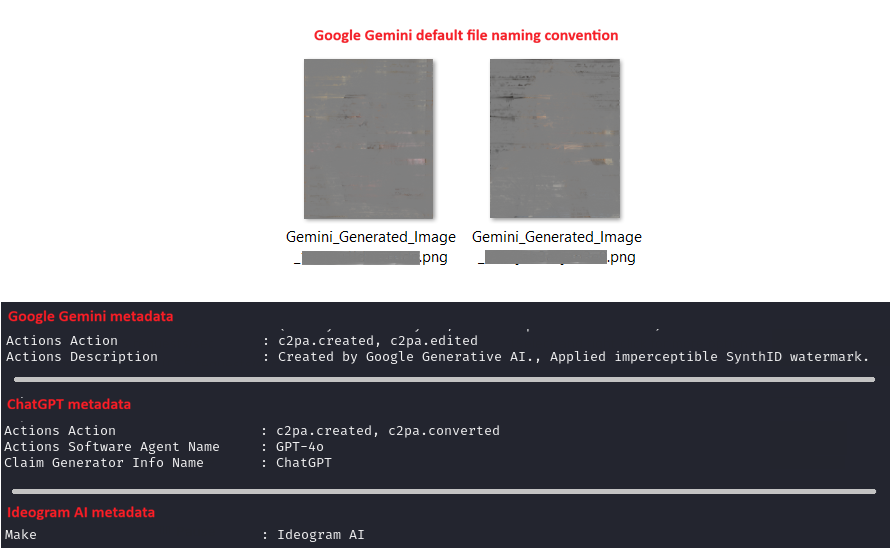
*LLM markers in images used by GreyVibe.
The use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance. A PowerShell-based remote access trojan named LegionRelay was also likely developed with assistance from AI tools, the researchers say. LegionRelay supports file theft, screenshot capturing, browser credential theft, Telegram and WhatsApp data exfiltration, and RDP access setup. Another malware used by GreyVibe is PhantomRelay, also a PowerShell RAT. The malware supports system fingerprinting, dynamic script loading, and PowerShell and Windows command execution.

*overview of malware and campaign associations.
Finally, the hackers employed the FallSpy Android spyware on the PrincessClub and Nebo campaigns, which is designed purely for collecting intelligence. The malware collects contact lists, call logs, device and network information, location data, media files, and SIM information. WithSecure notes that while GreyVibe activity is consistent with a nation-state operation, the threat actor "lacked the level of sophistication and operational discipline typically associated with mature nation-state actors." Furthermore, the PhantomRelay malware has been seen in cybercrime activity, although researchers could distinguish its usage from state-aligned operations. This led the researchers to believe that GreyVibe may include "current or former cybercriminal actors." Some evidence pointing to this theory includes the use in early and test samples of a unique ISO builder associated with a group of former TrickBot members (UAC-0098) that targeted Ukraine at the start of the Russian invasion. Furthermore, the threat actor uploaded development and test samples to a public scanning platform, which is not typical with nation-state actors. Additionally, a cryptocurrency miner was deployed on some victim machines. The researchers are unsure "whether former or current cybercriminal members have been absorbed into a state-backed group, operate independently but with state-directed tasking, or have formed a hybrid team involving state-affiliated and cybercriminal members." Organizations can set up defenses against GreyVibe's malicious activity by using the indicators of compromise (IoCs) provided by WithSecure.
- PhantomMail: Spear-phishing emails delivering malicious ZIP/RAR archives via Google Drive and 4sync links, using decoy PDFs or fake errors while deploying malware. The observed lures impersonated Ukrainian government, emergency, telecom, and energy entities.
- PhantomClick: Fake CAPTCHA/ClickFix pages disguised as Zoom and LAPAS sites trick victims into running self-infecting commands through fake Cloudflare verification prompts.
- PrincessClub: Fake Ukrainian adult/dating websites delivering FallSpy Android spyware and PhantomRelay/LegionRelay Windows malware. The operators used fake female Telegram personas and later added WebRTC-based live calls that could capture the victim's audio/video.
- DroneLink: Fake Ukrainian military charity websites themed around FPV drones and UAVs shared infrastructure and tooling with PrincessClub campaigns.
- Nebo: Fake “СПО НЕБО” Russian military communications login pages were likely designed to trick Ukrainian military personnel into believing they were accessing a Russian military terminal.
*LLM markers in images used by GreyVibe.
The use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance. A PowerShell-based remote access trojan named LegionRelay was also likely developed with assistance from AI tools, the researchers say. LegionRelay supports file theft, screenshot capturing, browser credential theft, Telegram and WhatsApp data exfiltration, and RDP access setup. Another malware used by GreyVibe is PhantomRelay, also a PowerShell RAT. The malware supports system fingerprinting, dynamic script loading, and PowerShell and Windows command execution.
*overview of malware and campaign associations.
Finally, the hackers employed the FallSpy Android spyware on the PrincessClub and Nebo campaigns, which is designed purely for collecting intelligence. The malware collects contact lists, call logs, device and network information, location data, media files, and SIM information. WithSecure notes that while GreyVibe activity is consistent with a nation-state operation, the threat actor "lacked the level of sophistication and operational discipline typically associated with mature nation-state actors." Furthermore, the PhantomRelay malware has been seen in cybercrime activity, although researchers could distinguish its usage from state-aligned operations. This led the researchers to believe that GreyVibe may include "current or former cybercriminal actors." Some evidence pointing to this theory includes the use in early and test samples of a unique ISO builder associated with a group of former TrickBot members (UAC-0098) that targeted Ukraine at the start of the Russian invasion. Furthermore, the threat actor uploaded development and test samples to a public scanning platform, which is not typical with nation-state actors. Additionally, a cryptocurrency miner was deployed on some victim machines. The researchers are unsure "whether former or current cybercriminal members have been absorbed into a state-backed group, operate independently but with state-directed tasking, or have formed a hybrid team involving state-affiliated and cybercriminal members." Organizations can set up defenses against GreyVibe's malicious activity by using the indicators of compromise (IoCs) provided by WithSecure.